Java4Shell: check AVX-512 VBMI hosts for OpenJDK Base64 flaw
Java4Shell (CVE-2026-114938) hits OpenJDK on AVX-512 VBMI x86-64 hosts; see which builds and CPUs are exposed, what sources disagree on, and mitigations.
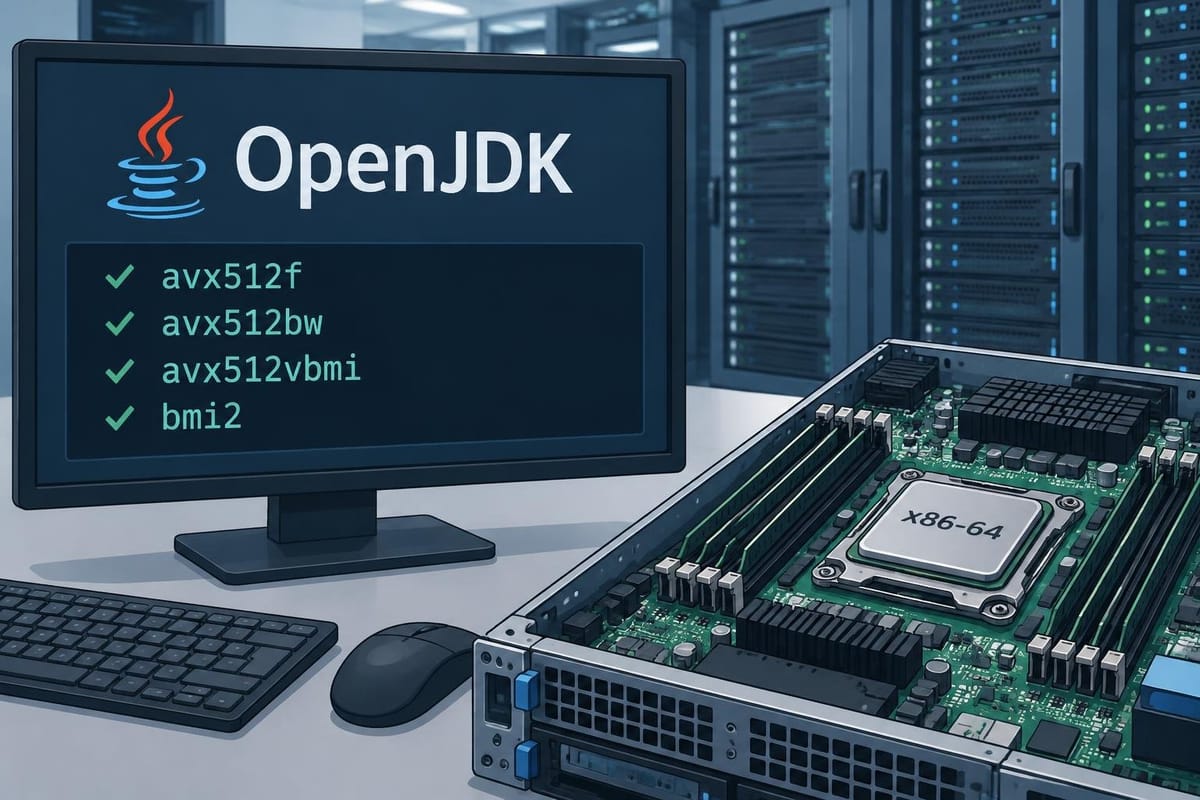
Calif researchers disclosed Java4Shell (CVE-2026-114938) on November 17, 2026. It is a heap memory-corruption bug in the hand-written assembly OpenJDK's HotSpot VM uses to speed up Base64 decoding. Calif rates it 9.2 (Critical) under CVSS 4.0 and says it demonstrated remote code execution against several widely used Java products. Per Calif, OpenJDK published an advisory and Oracle released a patch at 1:00pm PT the same day.
The bug matters only on a specific class of hardware: x86-64 CPUs with AVX-512 VBMI support. Calif says ARM64 is not affected. Amazon Linux's CVE page independently identifies the CVE as the OpenJDK Base64 issue, says it affects OpenJDK 17.0.6 and later, and rates it 8.8 under CVSS 3.1. Check your fleet for the CPU features first, then for the JDK build.
Who is exposed
Calif's affected-vendor list: Eclipse Temurin, Microsoft Build of OpenJDK, Azul Zulu, BellSoft Liberica, SAP SapMachine, Red Hat OpenJDK, Amazon Corretto, Oracle OpenJDK, Oracle Java SE and Oracle GraalVM for JDK.
All four CPU flags must be present. Calif lists these CPU families as meeting the requirement:
- Intel Xeon: Ice Lake, Sapphire Rapids, Emerald Rapids, Granite Rapids
- AMD EPYC and Ryzen: Zen 4 or newer
Calif's Linux check:
grep -m1 '^flags' /proc/cpuinfo | tr ' ' '\n' | grep -E '^(avx512f|avx512bw|avx512vbmi|bmi2)$'
The output must include avx512f, avx512bw, avx512vbmi and bmi2; otherwise the hardware is outside the reported scope. In virtual machines, what matters is the CPU feature set the guest sees, which can differ from the physical host.
Versions and fixes: sources disagree
Calif cites Oracle as listing these Java SE builds as vulnerable: 8u511b33-perf, 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3 and 27.0.1.0.3. Aikido's tracker lists Oracle Java SE 17, 21, 25 and 27 as affected, with fixes in 17.0.21.1, 21.0.13.1, 25.0.5.1 and 27.0.1.1, and says Java SE 8 and 11 are not affected by this CVE. That conflicts with the 8u build in Calif's list, and we could not reconcile the two. Amazon Linux likewise marks its Corretto 8 and 11 packages and the Amazon Linux 2 OpenJDK 7/8 packages as not affected, but marks java-11-openjdk on Amazon Linux 2 as "No Fix Planned".
The four lines are therefore not an exhaustive list. Amazon Linux says 17.0.6 and later are affected, and it lists fixed Corretto 17, 21, 25 and 27 packages on November 17 while marking the listed Corretto 22, 23, 24 and 26 packages as no fix planned. Those are non-LTS releases, so anyone running those packages should not expect a patch from Amazon for them and should move to a fixed line or use the mitigation flags below. If you run Java 8 from Oracle, treat the listed 8u build as something to check against Oracle's notes rather than dismiss.
Aikido, as of November 18, lists Amazon Corretto fixed builds 17.0.21.1.2, 21.0.13.1.2, 25.0.5.1.2 and 27.0.1.1.4. Amazon's page confirms fixed packages exist but does not independently establish those build numbers. For Eclipse Temurin Aikido listed no confirmed fix, and Oracle GraalVM's affected range was not confirmed. Vendors ship on their own schedules and build numbers differ, so use your vendor's fixed build, not Oracle's. Remember JDKs bundled inside applications, container base images and distribution packages such as openjdk-17.
Oracle's notes are linked from Aikido's post (for example the 17.0.21.1 release notes), and Calif links the OpenJDK advisory and Oracle's alert. Our reads of those pages returned HTTP 403, so we have not seen their contents.
What the bug is, and what an attacker must control
Per Calif, the assembly that handles the final characters mishandles a stray padding character (=) and computes a negative output length. That becomes a 64-byte write. In Calif's example, a 65-character input gets a 50-byte result array, and the write starts at offset 48, so 62 bytes land past the end. Java later rejects the input, but neighboring heap objects may already be corrupted. The out-of-bounds bytes are uncontrolled, and the attacker can influence where the write lands. Calif says the first in-bounds byte is fully controlled and the second is partially controlled.
Decoding Base64 is not by itself evidence of exposure. An attacker must get crafted input into a decoder that runs the intrinsic path, on a vulnerable build and CPU. Calif says turning the bug into code execution required heap grooming and a per-target approach: a route to the decoder, a way to read back responses and a workable heap layout. It describes spraying and retrying until the layout works, and says latency and jitter affect the attack. It rented a VM near its target to stabilize testing.
What Calif demonstrated
Calif reports remote code execution in default configurations. Pre-authentication: Keycloak, Atlassian Jira and Confluence, JFrog Artifactory, Jenkins and PingFederate. Post-authentication: Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit and Spinnaker. It also reports sample applications built on Apache Struts and Spring Boot. A client-side exploit, shared by samczsun, can compromise a Java program that opens a TLS connection to a malicious server. These are the researchers' claims from controlled tests; we have seen no independent reproduction. Calif says it used AI to find and weaponize the bug. Amazon's description is narrower than Calif's headline: a JVM crash for unauthenticated users, or code execution by an authenticated low-privileged user in certain application environments.
Exploitation status
As of November 17, Aikido said it had seen no reports of exploitation in the wild. Calif's write-up notes buffering proxies can disrupt some attack profiles, since some grooming needs partial request bodies, and nginx buffers request bodies by default. That is a partial hedge, not a fix, and does not cover the client-side case.
What to do
- Inventory every Java runtime on x86-64 hosts with the four CPU flags above, not just 17, 21, 25 and 27. Include non-LTS releases, Oracle's listed 8u build, bundled JDKs and container images, and check each against your vendor's advisory.
- Update to your vendor's fixed build. Prioritize internet-facing services and the products Calif named.
- Where you cannot patch, Calif lists two JVM flags:
-XX:-UseBASE64Intrinsicsdisables the hardware-accelerated Base64 path, and-XX:UseAVX=2disables AVX-512. Use the second only on x86-64; Calif says OpenJDK on ARM does not recognize it and will fail to start. - Restart services after updating, since running JVMs keep the old code.
We could not verify the CVE record in NVD or a CISA KEV listing. Whether Temurin and other vendors have shipped fixes, and how Oracle's Java SE 8 listing resolves, remain to be confirmed against vendor advisories.
Comments ()