Alpine OpenSSH flaw *sshole under attack; update, then restart sshd
Attackers exploited OpenSSH's *sshole flaw on musl Linux days after 10.6p2; learn who is exposed, how Alpine backports work, and why sshd needs a restart.
Attackers began trying to exploit "*sshole" (CVE-2026-123158), an OpenSSH authentication bypass on musl-based Linux systems, on November 5, the day OpenSSH 10.6p2 shipped, and successful exploitation was recorded the next day, BleepingComputer reported on November 9. Threat-intelligence firm GreyNoise logged 16 successful exploitation chains, and in one case an attacker gained root and installed a Python command-and-control implant, according to that report.
The consequence for administrators: installing the patched package is not enough. The running sshd must be restarted, and on Alpine the package revision, not the OpenSSH version string, shows whether a host is fixed.
OpenSSH's release notes call 10.6p2, released November 5, a critical workaround for a password authentication bypass affecting some Linux systems built and run with PAM disabled. The project says it considers the root cause "outside sshd," though it is exploitable through sshd and can be avoided there. The bug was reported by Özgün Kültekin of Wakefield. BleepingComputer's original report says the behavior dates to a 2016 username-enumeration fix, interacting with how musl's crypt() reports errors. A separate write-up on sshhole.com gives the researcher's timeline.
Who is exposed: per Kültekin's conditions as relayed by BleepingComputer, all of these must hold. OpenSSH runs on a musl-based system (Alpine, OpenWrt, Buildroot, Yocto); PAM is disabled, as in Alpine's openssh-server package; password authentication is on; at least one account has * as its password hash; and another account has a valid hash. CyCognito adds that the valid hash must be SHA-crypt (5 or 6) and that accounts locked with ! are unaffected. Glibc systems such as Debian, Ubuntu and Fedora, and PAM-based setups, are not affected. Alpine's official AWS and Azure images ship an 'alpine' account with passwordless doas, which could turn a login into root.
Fix status: CyCognito reports Alpine released patched openssh packages for edge and branches 3.16 through 3.24. Alpine backported the fix, so patched packages keep older upstream version numbers (CyCognito cites 10.3_p1-r2 on 3.24 and 10.0_p1-r11 on 3.22). Check the package release, not the version string. We did not independently review Alpine's advisory.
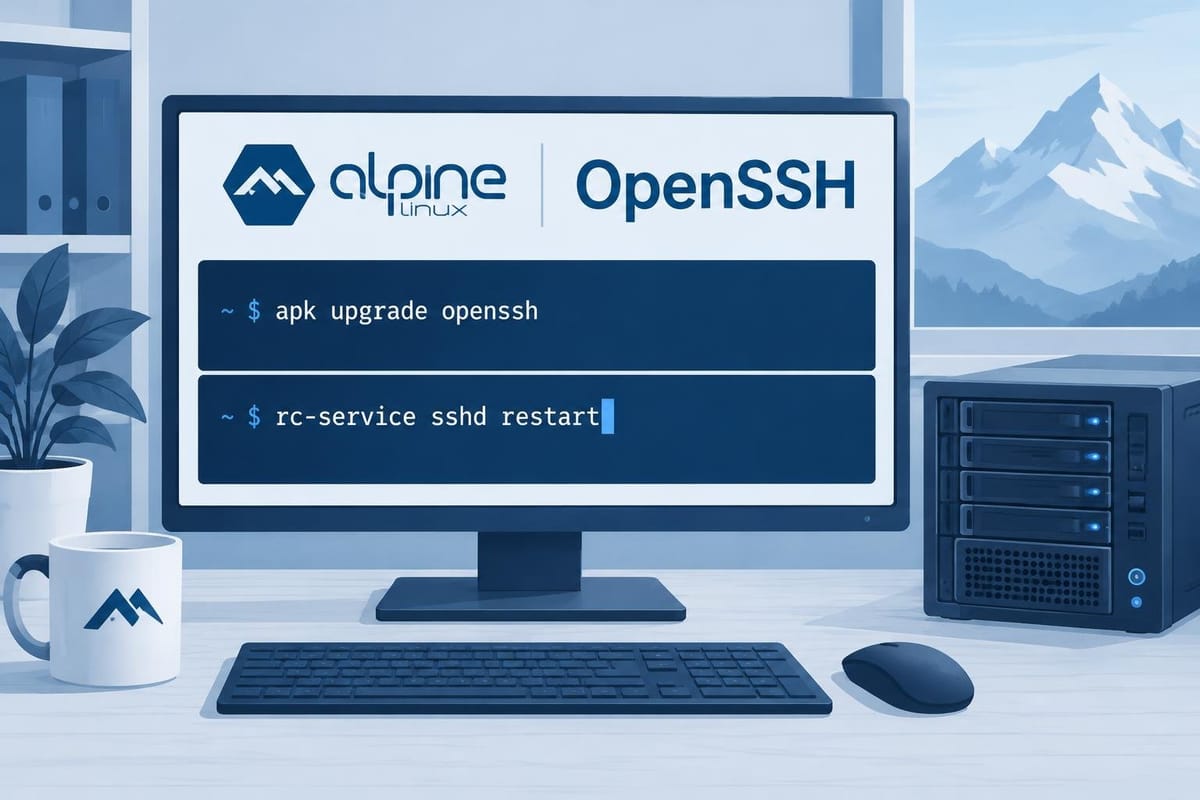
Steps: on Alpine, run apk upgrade openssh, then restart sshd (on OpenRC, rc-service sshd restart). If you cannot patch, set PasswordAuthentication no and restart. To look for compromise, run grep "Accepted password" /var/log/messages and check for successful password logins to accounts whose /etc/shadow field is *. BleepingComputer also advises checking for unexpected authorized SSH keys and TAC Agent files or startup services.
Not yet known: whether other musl distributions such as OpenWrt, Buildroot and Yocto images have shipped fixed builds, and whether musl will change the underlying behavior; Ars Technica quotes musl developer Rich Felker as saying it is not a musl bug but planned changes were already intended.
Comments ()