Four in five enterprise AI deployments still lack a named owner — what teams may have to fix now
Why most enterprise AI deployments still lack a named owner, and what teams need to fix in logs, inventory, procurement, and oversight.
Four in five enterprise AI deployments still lack a named owner — what teams may have to fix now
The sharpest thing about the latest enterprise AI accountability story is not the technology. It is the paperwork gap.
A reported industry study says four in five enterprise AI deployments still lack a named owner. That matters because the operational work around AI — inventory, logging, approvals, review, rollback, and vendor oversight — tends to fail first when no one is clearly accountable. The immediate consequence is not just organizational drift. It is that companies may be unable to prove who approved a system, what controls were in place, or what happened when something went wrong. TechTimes report
The reporting lines up with a broader legal shift in Europe, but the law is more nuanced than a single universal command. The EU AI Act — Regulation (EU) 2024/1689 — creates role- and risk-based obligations for providers and deployers, and the European Commission’s guidance translates those obligations into practical requirements such as documentation, traceability, and oversight. In other words: the Act does not simply say “every AI system must have one owner.” It says responsibility, records, and controls matter more as systems become more consequential and as a company’s role in the AI supply chain changes. EUR-Lex: Regulation (EU) 2024/1689 · European Commission AI Act overview
What the law actually pushes teams to build
For companies deploying AI, the practical effect is that governance stops being a policy page and becomes an operational system.
The AI Act’s obligations vary by category and by role, but the common thread is traceability. For higher-risk systems, the law is more explicit about recordkeeping, documentation, human oversight, and quality-management expectations. Those duties do not apply identically to every use case, but they do make one thing clear: if a system is important enough, the company must be able to show how it was assessed, controlled, and monitored.
That is where the reported “no named owner” gap becomes operationally important. A missing owner usually means no one is consistently responsible for the following:
- maintaining the inventory of AI systems and use cases;
- deciding whether a system is in scope for stricter review;
- defining what logs must be captured and how long they are retained;
- collecting vendor documentation before rollout;
- tracking approvals, exceptions, and rollbacks;
- coordinating security, legal, procurement, and product decisions.
The first fix is a live inventory
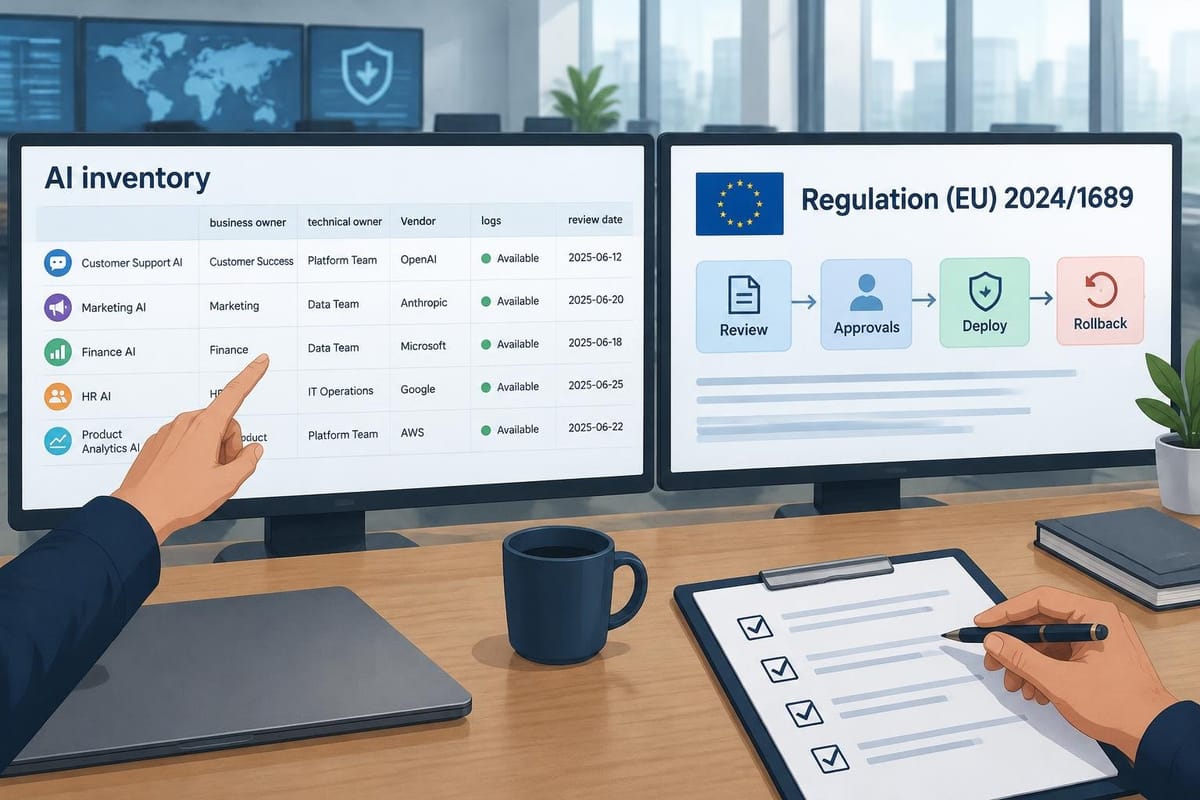
If teams want a control stack that can survive an audit or an internal incident review, the first requirement is a real inventory — not a spreadsheet that is assembled after a problem surfaces.
A useful inventory needs to connect the model or tool to the business process it affects, the people responsible for it, and the evidence trail behind it.
- system or use-case name
- business owner
- technical owner
- vendor or model source
- intended use
- data categories used
- deployment environment
- logging enabled: yes/no
- risk classification
- approval record
- review date
That list is not legal boilerplate. It is the minimum structure needed to answer basic questions under pressure: what is running, who approved it, and where is the supporting evidence?
Logging is no longer just a debugging feature
The Commission’s guidance and the Act’s traceability logic both point to the same practical conclusion: logs are evidence.
For teams running AI in production, that means log design has to capture enough context to reconstruct what the system did. At minimum, teams generally need to preserve details such as the model or version used, the input and output, the time of the action, any human override, and the workflow or application context. If logs are too short-lived, too sparse, or too hard to correlate with a specific deployment, they are unlikely to support later review.
That becomes especially important as companies move from simple chat interfaces to agentic workflows and embedded automation. In those systems, a failure may not be one model response. It may be a chain of prompts, tool calls, and handoffs.
Procurement is where governance often breaks first
The strongest counterargument to all of this is straightforward: better paperwork does not make a model safer.
That is true. A contract clause will not prevent a hallucination, and a policy document will not stop misuse.
But procurement is where many control failures begin. If the buyer cannot get clarity on model limitations, logging behavior, update policies, incident response, or data-processing terms, then the deployment is already opaque. In that sense, the AI Act’s practical effect is not just regulatory. It pushes companies to ask vendors for evidence before rollout instead of after an incident.
For product, security, legal, and procurement teams, the relevant artifact list usually includes:
- system or model documentation;
- risk classification;
- security controls;
- data-processing terms;
- update and deprecation notices;
- human-oversight design;
- incident escalation path.
Why “named owner” is the right operational conclusion
The headline statistic is not, by itself, a legal finding. It is a reporting signal about how fragile enterprise AI governance still is.
The best-practice conclusion is simpler: one person or function has to be able to say yes or no.
That does not mean every AI system needs a single engineer wearing every hat. It means someone must be accountable for approval, rollback, review timing, and escalation. Without that, responsibility gets split across product, ML engineering, security, legal, and procurement — and split responsibility often behaves like no responsibility when something goes wrong.
That is the practical lesson behind the legal shift: governance is a chain of custody, not a slogan.
What breaks when no one owns the system
The absence of a named owner is not only a compliance problem. It also creates operational risk.
If no one is clearly responsible, then:
- model updates can ship without a review sign-off;
- logs may not be retained long enough to reconstruct a failure;
- shadow AI use can stay invisible inside business units;
- procurement can approve tools without the controls security needs;
- incident response can stall while teams argue over ownership.
That is why the ownership gap is more than bureaucracy. It is the first missing control that makes the rest of the control stack unreliable.
The strongest cautionary note
There is also a real danger that companies respond to the AI Act by producing more documents without changing how systems are built or monitored.
That criticism deserves to be taken seriously. Compliance programs can become a paper chase, especially when the business wants speed and the legal team wants evidence. A polished inventory alone does not guarantee that a model has been evaluated properly or that an unsafe workflow will be caught in time.
But the opposite mistake is just as common: treating AI as a feature instead of an operational system.
If a company cannot identify the owner, the deployment path, the log source, and the approval record, then it probably cannot explain the system’s behavior either. The best governance programs will do both: produce the paperwork and change the way systems are built and operated.
What teams may have to do first
For companies that are now realizing they are underprepared, the most useful sequence is usually:
- Name an accountable owner for every AI system or use case.
- Build or repair the system inventory.
- Define what gets logged and how long it is retained.
- Collect vendor documentation and contract evidence.
- Map each system to a risk tier and review cadence.
- Test rollback and human-override procedures.
That is not a complete compliance program. It is the minimum scaffolding for one.
The surprise in the reported ownership gap is not that enterprises are moving quickly. It is that many are still treating AI like a feature layer rather than an operational system with an owner, an audit trail, and a failure mode.
The EU AI Act does not eliminate that problem. It makes it harder to ignore.
Sources
- TechTimes report on the ownership gap: https://www.techtimes.com/articles/329368/20261022/ai-decisions-outrun-accountability-four-five-enterprise-deployments-have-no-named-owner.htm
- Regulation (EU) 2024/1689, European Union AI Act: https://eur-lex.europa.eu/eli/reg/2024/1689/oj
- European Commission AI Act overview: https://digital-strategy.ec.europa.eu/en/policies/regulatory-framework-ai
Comments ()