Anthropic’s Claude Code change looks narrower than the complaints — but the guardrails still bite
What the record actually supports about Claude Code’s safety defaults, permissions pressure, and Goldman Sachs’ restrictions.
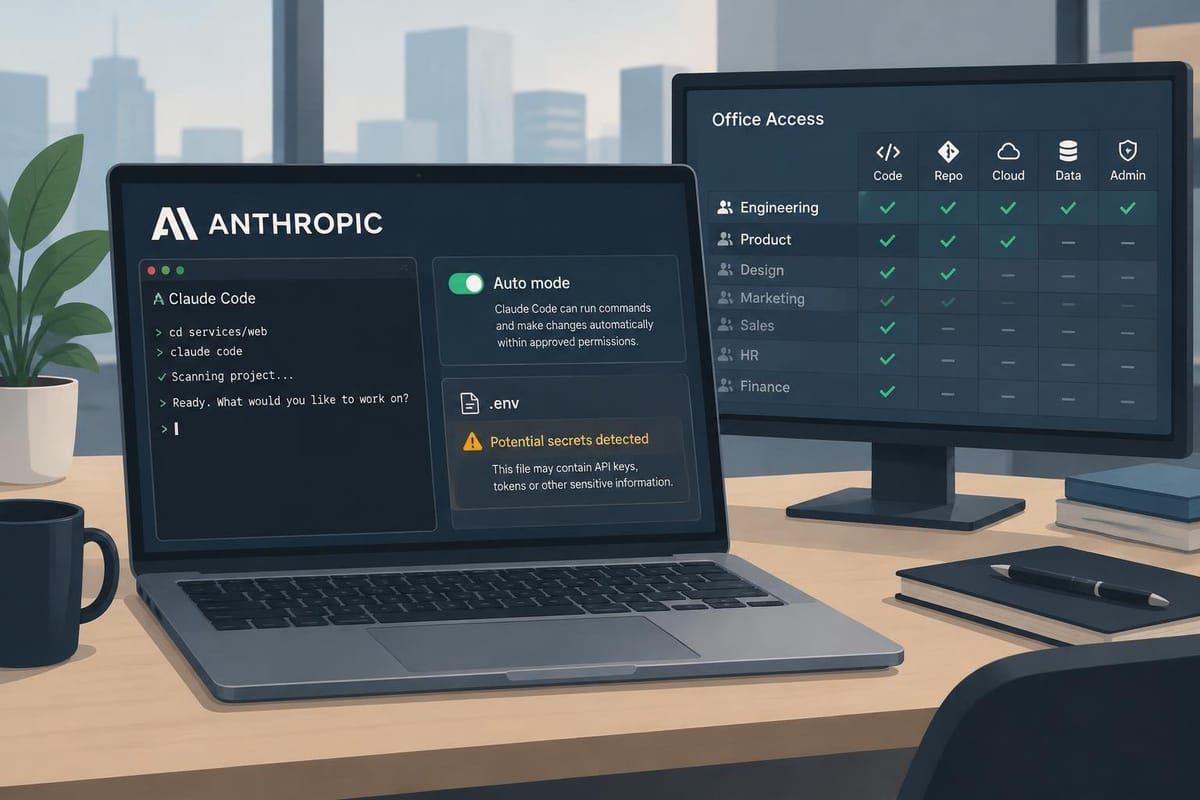
Anthropic’s latest Claude Code controversy is less about a single dramatic ban than about where the product’s safety logic now draws the line.
The public record captured for this story does not show Anthropic issuing a formal policy memo announcing a new ban on reverse engineering or game cloning. What it does show is an Anthropic employee, posting on Hacker News, saying the team has not historically done secret scrubbing in Claude Code, that it is looking into preventing that, and that “everyone should be using auto mode instead” because it is “safer” than manually maintained allowlists. The same thread shows users arguing that the tool can be too aggressive or too probabilistic for work where they want deterministic boundaries. Source: https://news.ycombinator.com/item?id=50407882
That matters because the argument is no longer just about whether Claude Code can help with ordinary software tasks. The actual tension in the public discussion is between two ideas of what a coding agent should be allowed to do:
- a permissive assistant that helps with broad engineering work but still needs user-managed rules, and
- a more opinionated system that tries to steer users away from risky actions, even when those actions may be legitimate in some contexts.
The evidence here supports the second point only indirectly. Users in the Hacker News thread said they were concerned about secret handling, allowlists, and the model’s willingness to proceed without clear human control. One commenter pointed to deterministic boundaries and sandboxing; another said the model had pushed toward actions they would not have allowed. Those are user reports and opinions, not Anthropic’s written policy. Source: https://news.ycombinator.com/item?id=50407882
The clearest product-specific statement in the capture is the employee’s own note that Claude Code has not done secret scrubbing and that the team is looking at ways to prevent it. That is a narrower claim than “Anthropic tightened Claude Code around reverse engineering,” and it is the safest way to describe the public evidence. The thread also links to Anthropic documentation about settings and permissions, which suggests the company wants users to rely more on built-in modes and less on hand-built allow/deny lists. Source: https://news.ycombinator.com/item?id=50407882
There is another important part of the story: this is not happening in isolation. Goldman Sachs, according to a report from The State of AI, has restricted Anthropic’s Claude Code and Microsoft’s GitHub tools to its engineers, cutting off traders and bankers after an internal review of productivity and risk concerns. The report says the October guidance limits third-party agents that can write and run code by themselves, while Goldman’s internal AI assistant remains available more broadly. Source: https://www.thestateofai.com/news/goldman-sachs-claude-code-traders-bankers
That Goldman move is a practical illustration of where the market is headed. Financial firms are not just asking whether a coding agent is clever; they are asking who is allowed to use it, what data it can touch, and whether the person using it can actually review what it does. The State of AI report says traders had used the tools to monitor client flows and build market models, which is exactly the kind of workflow that becomes sensitive once code-writing and code-running collapse into the same interface. Source: https://www.thestateofai.com/news/goldman-sachs-claude-code-traders-bankers
Taken together, the HN thread and the Goldman report point to a more mundane but more consequential reality than the initial online chatter implied. Anthropic’s public-facing behavior in the captured material is not a clean “game cloning crackdown.” It is a combination of safer-default rhetoric, open questions about secret handling, and stronger pressure toward auto mode and permissions discipline. Meanwhile, enterprise customers like Goldman are drawing their own hard boundaries around which employees can use agentic coding tools at all.
That leaves legitimate workflows in a gray zone, but the gray zone is narrower than the original framing suggested. Based on the sources captured here, the strongest claim is not that Anthropic has formally targeted reverse engineering as a category. It is that Claude Code is being pushed toward stricter safety and permissions defaults, and that shift is beginning to collide with how some users expect to control the tool.
For developers, the practical takeaway is simple: if your workflow depends on manually curated allowlists, secret-adjacent operations, or agent behavior you can fully predict, the product direction in the public record points the other way. Anthropic’s own employee is nudging users toward auto mode, and enterprises are already deciding that not everyone should get the same access to coding agents. Sources: https://news.ycombinator.com/item?id=50407882 and https://www.thestateofai.com/news/goldman-sachs-claude-code-traders-bankers
What the record supports
- Anthropic employee comment: Claude Code has not historically done secret scrubbing, and the team is looking into preventing that. Source: https://news.ycombinator.com/item?id=50407882
- Anthropic employee comment: users should be using auto mode instead because it is safer than manual permission rules. Source: https://news.ycombinator.com/item?id=50407882
- Goldman Sachs restriction: Claude Code and GitHub were restricted to engineers under updated internal guidance. Source: https://www.thestateofai.com/news/goldman-sachs-claude-code-traders-bankers
- Goldman context: traders and bankers had been using the tools for client-flow tracking and market modeling. Source: https://www.thestateofai.com/news/goldman-sachs-claude-code-traders-bankers
The public evidence reviewed here does not support a crisp, first-party Anthropic statement saying it has banned reverse engineering or game cloning as such. What it does support is a narrower and more defensible conclusion: Claude Code is being pushed toward stricter safety and permissions defaults, and that shift is beginning to collide with how some users expect to control the tool.
Comments ()